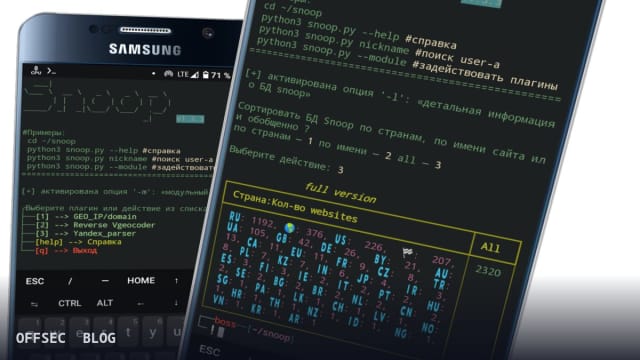
snoop is an OSINT username-search utility that checks a single nickname against roughly 5,400 public websites, built for authorized investigations, blue-team triage, and research into exposed digital footprints.
| Tool | snooppr/snoop — Python-based OSINT nickname search engine with a database of ~5,400 websites and optional GEO/IP plugins |
| Category | OSINT / username enumeration / web scraping |
| Primary Use | Mapping where a given nickname appears across public services during authorized investigations, CTF work, and self-audits of one's own digital footprint |
| Safe Use | Use only on yourself, consenting clients within scoped authorized assessments, missing-person or fraud investigations handled by proper authorities, and lab research — not for stalking or unauthorized surveillance of third parties |
| Telemetry Note | Every query causes direct HTTP requests from your IP to ~5,400 sites, many of which log visitor patterns; defenders can detect mass nickname-probing through abnormal request rates from single sources against signup/profile endpoints |
snoop is an open-source intelligence tool whose core function is deceptively simple: you hand it a nickname, and it queries an internal database of roughly 5,400 websites to report where that username appears as a registered account. The project, hosted at snooppr/snoop and written in Python, positions itself explicitly in the OSINT tradecraft space — its topic tags include osint, username-search, blueteam, redteam, and pentest — and its README frames the work as research into searching and processing publicly available data on the internet. For professionals who regularly pivot from a single identifier to a fuller picture of an adversary's or subject's online presence, this is the same niche occupied by tools like sherlock or whatsmyname, but with a database the author claims is roughly an order of magnitude larger.
The README is primarily in Russian, with community-maintained translations into English, Spanish, German, Chinese, and French, which tells you something about the project's audience and its grassroots maintenance model. It was created on February 14, 2020, and the repository has accumulated over 4,000 stars, indicating sustained interest. The author claims the database covers approximately 5,400 sites, compared against Whatsmyname (~600), sherlock (~400), SpiderFoot (~350), and Namechk (~100) per the badges in the README. Treat those comparative numbers as self-reported marketing rather than audited fact, but the raw websites.md database file is published in the repository, so the coverage claim is at least verifiable by inspection.
Architecturally, snoop is a parallel scraping engine. The --pool/-p flag lets you manually set the number of worker processes from 1 to 300, and the tool auto-optimizes this by default, adapting to the host machine's CPU and RAM. The --quick/-q mode is described as fast and aggressive: it skips re-processing resources that failed on the first pass, which speeds up a run at the cost of a slightly higher Bad_raw error count. A --time-out/-t flag (default 9 seconds) controls per-site wait windows. This concurrency model is the standard approach for this tool class — fire asynchronous requests at hundreds of profile-lookup endpoints, then diff responses against known found/not-found signatures — and the README's emphasis on pool tuning suggests the bottleneck is I/O saturation rather than parsing logic.
Search scoping is where snoop shows more regional awareness than most competitors. The --include/-i and --exclude/-e flags accept country codes and can be stacked, so -i US -i UA restricts the sweep to US and Ukrainian services while -e RU -e WR excludes Russia and worldwide sites from results. The --country-sort/-c flag orders output by country rather than alphabetically. This matters operationally because a regional focus dramatically cuts noise and runtime; querying 5,400 endpoints when 200 are relevant to your case wastes time and generates unnecessary traffic. The README explicitly calls snoop a tool that accounts for the CIS region — a coverage gap in many Western-centric username checkers.
The CLI surface is well documented in the README. --list-all/-l prints detailed information about the site database, letting you enumerate exactly what will be queried before you run a search. --site/-s narrows the run to a single named site and can be repeated. --found-print/-f suppresses everything except positive hits, which is what you want in most operational contexts. --verbose/-v gives full per-site output for debugging, --no-func/-n disables colors, browser auto-open, and country flags for clean terminal capture, and --save-page/-S archives discovered profile pages as local html files — slower, but it preserves evidence for a report. The --userlist/-u flag accepts a file of multiple usernames for bulk processing with additional reports.
Beyond plain username lookups, snoop ships a plugin system exposed through --module/-m, covering IP/GEO/YANDEX functionality. The README demonstrates a GEO_IP/domain plugin that produces geolocation reports in csv, txt, CLI, and HTML-map formats built on OSM — useful for enriching an IP or domain indicator with spatial context during an authorized investigation. A Yandex_parser plugin searches a dozen nicknames and reports results, and a Reverse Vgeocoder plugin extracts geocoordinates from dirty mixed data — digits, letters, special characters — places markers on a map, and labels them with nearby settlements. These plugins push the tool beyond pure username enumeration into lightweight geospatial analysis, which is a genuine differentiator in this tool category.
Installation follows two paths. Ready-made release builds for Windows and GNU/Linux are distributed through the GitHub releases page and run on a clean machine with no Python or dependency installation — a deliberate design choice that also means you should verify binaries before running them, since prebuilt executables from any project deserve that baseline scrutiny. Building from source is conventional: clone the repo, install python3 and python3-pip via apt-get, then python3 -m pip install -r requirements.txt. The README notes Python 3.7+ as the minimum and recommends the fonts-noto-color-emoji package so country flags render correctly in the terminal. Android support exists via Termux with a separate installation path, macOS is experimental, and both iOS and WSL are explicitly unsupported — with an amusing warning to use cmd directly on Windows rather than WSL.
The tool is licensed under a non-standard NOASSERTION license per GitHub metadata, which is worth flagging: the README also mentions a paid Snoop full version obtainable through donation, meaning some capabilities (like certain HTML map reports) sit behind a purchase rather than the open repository. The free version still provides the core database search and the --web-base/-w flag that connects to a dynamically updated web database of 5,400+ sites, so the essential functionality is available without paying. Practical housekeeping flags include --autoclean/-a to purge reports and cache, and --update/-U to pull the latest version — both worth running regularly since site databases in this tool class rot quickly as services change their profile URL structures.
For blue teams and defenders, snoop has a genuine dual-use story. Running it against your own organization's naming conventions reveals which employee usernames are enumerable across public platforms — reconnaissance an attacker would perform in the first minutes of a targeted campaign. That visibility lets you advise staff on handle hygiene and gives threat-intel teams a repeatable method for correlating a suspicious persona across services during incident response. The telemetry consideration cuts both ways: a full sweep generates thousands of outbound requests from a single IP in minutes, which is noisy from the operator's perspective and, from the defender's perspective at a target service, manifests as a burst of profile-page requests that never navigate anywhere — a pattern worth rate-limiting and logging at scale.
The responsible-use framing cannot be overstated. A tool that links a nickname to accounts across thousands of services is a stalking instrument in careless hands, and the README's low-barrier pitch — download, enter a target, get results — means the operator bears full responsibility for lawful basis. Appropriate contexts are explicit: authorized penetration tests with OSINT in scope, internal footprint audits, CTF exercises, missing-person and fraud casework through legitimate channels, and academic research on identifier correlation. Used that way, snoop is one of the most comprehensive publicly documented nickname-correlation engines available, and its regional database depth makes it particularly valuable for investigations involving CIS-region infrastructure and services that Western tooling underserves.
snooppr/snoop.Educational analysis for authorized security professionals. Use only in controlled, authorized environments.
Related coverage


0 comentários:
Post a Comment
Note: Only a member of this blog may post a comment.