Skip to content
>_offsec / blog
ArticlesToolsEventsResearch / Bounty
  • RSS ↗
OFFENSIVE SECURITY · HACKER COMMUNITY

OffSec Blog

Research. Reverse engineering. Exploitation.
Knowledge built in the lab. Shared with the community.

Read the research ↗Open the toolbox →
Red Team — a shadowed figure in a crimson hood RED TEAM OFFSEC COLLECTIVERED / TEAMRESEARCHRESIST
RESEARCH / REVERSE / REPEATEST. 2015
  • Home
    • RESEARCH TRACKS
      • WEB SECURITY
      • REVERSE ENGINEERING
      • MALWARE ANALYSIS
      • CTF / CRACKMES
    • SECURITY TOOLS
      • Assessment Tools
      • Privacy
      • Privacy Guides
      • Lab Practice
    • ONLINE UTILITIES
      • Website Testing
      • Whois
      • IPAddress
      • Practice Lab
      • Reverse DNS Lookup
      • Network Mapper
      • IP Geo Location
      • Search Engine
      • DNS Resolver
      • HTTP Check
      • Central Ops
      • Wayback Machine
      • Internic
      • Statistics Of World In Real Time
      • NetCraft
      • DnsDumpster
    • PRIVACY RESOURCES
      • Privacy Tools
      • Prism-Break
      • Privacy Checklist
    • RESOURCES
      • Resources
      • Tools
      • Research Notes
      • Search Operators
    • LIBRARY
      • Tool Index
      • Security Tools
      • Movies
      • Projects
      • Wallpapers
    • CONNECT & LEARN
      • Community
      • Global events 2026
      • Exploit research and bug bounty

LATEST TRANSMISSIONS /

Follow via RSS ↗
Showing posts with label Reverse Engineering. Show all posts

Monday, October 19, 2026
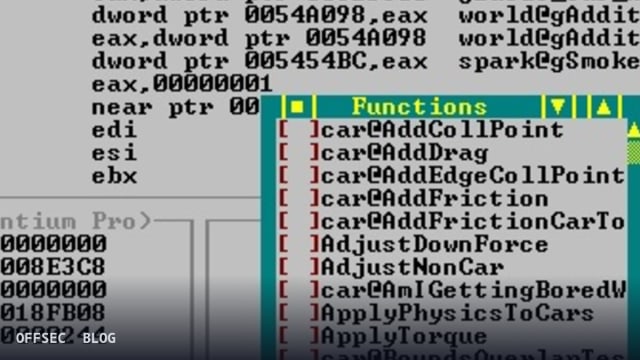
dethrace for rebuilding the 1997 Carmageddon engine through reverse engineering

2:25:00 AM Malware Analysis, Reverse Engineering No comments

Open this article to continue reading.

Read article

FAT for firmware identification, extraction and emulated analysis of IoT device images

12:25:00 AM CVEs, Malware Analysis, Reverse Engineering, Security Tools No comments

Open this article to continue reading.

Read article

Sunday, October 18, 2026

drakvuf-sandbox for agentless automated malware analysis

4:23:00 AM Malware Analysis, Reverse Engineering No comments

Open this article to continue reading.

Read article

cwe_checker for finding vulnerable patterns in binary executables
2:24:00 AM CVEs, Malware Analysis, Reverse Engineering, Security Tools No comments

Open this article to continue reading.

Read article

Thursday, October 15, 2026

Qu1cksc0pe for static triage of suspicious binaries across Windows, Linux, macOS and Android
4:24:00 PM Malware Analysis, Reverse Engineering No comments

Open this article to continue reading.

Read article
Older Posts Home

Search

Blog Archive

Top 75 Hacker Blogs

Explore the security community ↗Hacker blogs directory · Feedspot

Popular Posts

  • pbtk for recovering and fuzzing Protobuf schemas in reverse engineering work
    pbtk is a GUI-driven toolkit that extracts Protobuf structures from Java, C++, and web targets back into readable .proto files, then lets...
  • Inside rea: agent-driven reverse engineering from app behavior to native binaries
    rea wires AI agents and a CLI into local reverse-engineering workflows, decompiling native binaries and mapping JavaScript applications fo...
  • Inside NTDLL-reconstruction: flipping between hooked and clean ntdll stubs on demand
    NTDLL-reconstruction is a small C library demonstrating a userland EDR evasion technique that lets an operator flip between hooked and un...
  • AiSOC for self-hosted AI-driven security operations and alert triage
    AiSOC is an open-source, self-hostable AI Security Operations Center that ingests telemetry, correlates alerts, and lets auditable AI agen...
  • USBArmyKnife for close-access red team hardware operations
    USBArmyKnife turns cheap ESP32-S3 dongles into a programmable close-access platform combining DuckyScript HID, mass storage emulation and...
  • CyberStrike for autonomous AI-driven penetration testing
    CyberStrike is an open-source AI agent harness that turns an existing LLM subscription into a methodology-driven penetration testing assis...

Build your lab

VMwareVirtualBoxParallels DesktopQEMUBoot Camp

Categories

#SnowdenActive Directory AttacksAI SecurityAnalysisAndroidAndroid HackAndroid PentestAnonimatoAnonymityAnti-ForensicAnti-Forensic ToolsAnti-GovernmentAnti-SystemApacheAPI HackingAPKARMAssemblyAttack MapAuditing ToolAutomation ToolsAvKillAWS PentestBackdoorBindBlue TeamBlueTeamBluetoothBotbotnet/DDoSBountyBrute ForceBug BountyBypassCertificateCheat SheetCloud ForensicsCloud PentestCloud SecurityCoursesCryptographyCTF & CrackmesCTF EngineCVEsCyber ForensicsCyber WarData BaseDeepWebDevSecOpsDFIR & ForensicsDisassemblerDLL HijackingDns EnumerationDns ReconDns SpoofDocumentaryDoSDownloadsDUMPEmail HackingEncrypted DNSEngenharia ReversaEnumerationEvasionEXIFExploitExploitationExploitation ToolsExposed LeakedFakeFilmes e DocumentáriosFingerprintFirewallFootprintFrameworksFuck The SystemFuzzerGeoIPGoogle HackingHacker Operating SystemsHackersHackers NewsHackers ToolsHackingHacking Ebook'sHacking VídeosHacktivismHardeningHardwareHardware & WirelessHardware HackHiddenHIDSHoneypotsHow to exit the MatrixIDSIDS/IPSIncident ResponseInformation GatheringiOSIoTJAVAKaliKali LinuxKeyloggerLabsLeakedLeaksLearning ResourcesLeave The MatrixLinuxLinux SystemMacMalwareMalware AnalysisMetaSploitMind MapMIPSMITMMobile SecurityMonitoringMoviesNetworkNetworkingNew World OrderNmapOffensive PoliticsOffensive SecOffSecOffSec Exclusive ToolsOpen Your MindOpenSSLOs SecOSINT ToolsOWASP ZAP ScannerPassword CapturePassword CrackingPasswordsPayloadPCCPDFPentestPentest ToolsPhishing AttacksPhonesPHPPort ScanPost-ExploitationPost-Exploitation ToolPowerShellPr1v8PrivacidadePrivacyPrivacy & AnonymityPrivilege EscalationProjectsProxyPythonRansomwareRATRecon & OSINTRecover File and Disk AnalyzerRed TeamRedesRemoteReverseReverse EngineeringReverse ShellRFIDRootkitScan ToolsSecuritySecurity Ebook'sSecurity ToolsSeriadosSeriesShellShell PHPShellcodeShodanSnifferSocial EngineeringSource CodeSpoofingSQLinjectionSSLStealerSteganographyStress TestingStudySubdomain DiscoverySysInternalsTelnetThe Theory of ConspiracyThreat IntelligenceToolsTorTrojanTutorialsUnix SystemURL InspectorUsb BootVirtual MachineVirusVoIPVPNVulnerabilitiesVulnerability AnalysisWAFWeb ApplicationsWeb PentestingWeb SecurityWhoisWifi-HacksWindowsWireless HackingWord ListWordPressX86XSS
>_offsec / blog

Hack. Learn. Share.
Independent knowledge for the offensive security community.

Learning resourcesCommunityRSS feed ↗Back to top ↑
© 2026 OffSec Blog · Established 2015OFFSEC COMMUNITY / POWERED BY BLOGGER